SIEM testing and attack simulation

Prove your SIEM detects the attack, before a real attacker tests it for you.

APEX JediSyslogger generates realistic security logs from simulated firewalls, servers, cloud services and identity systems, injects attack scenarios on demand and sends them to your SIEM. Its built-in detection engine shows what should be detected, so you can see exactly where your rules fall short.

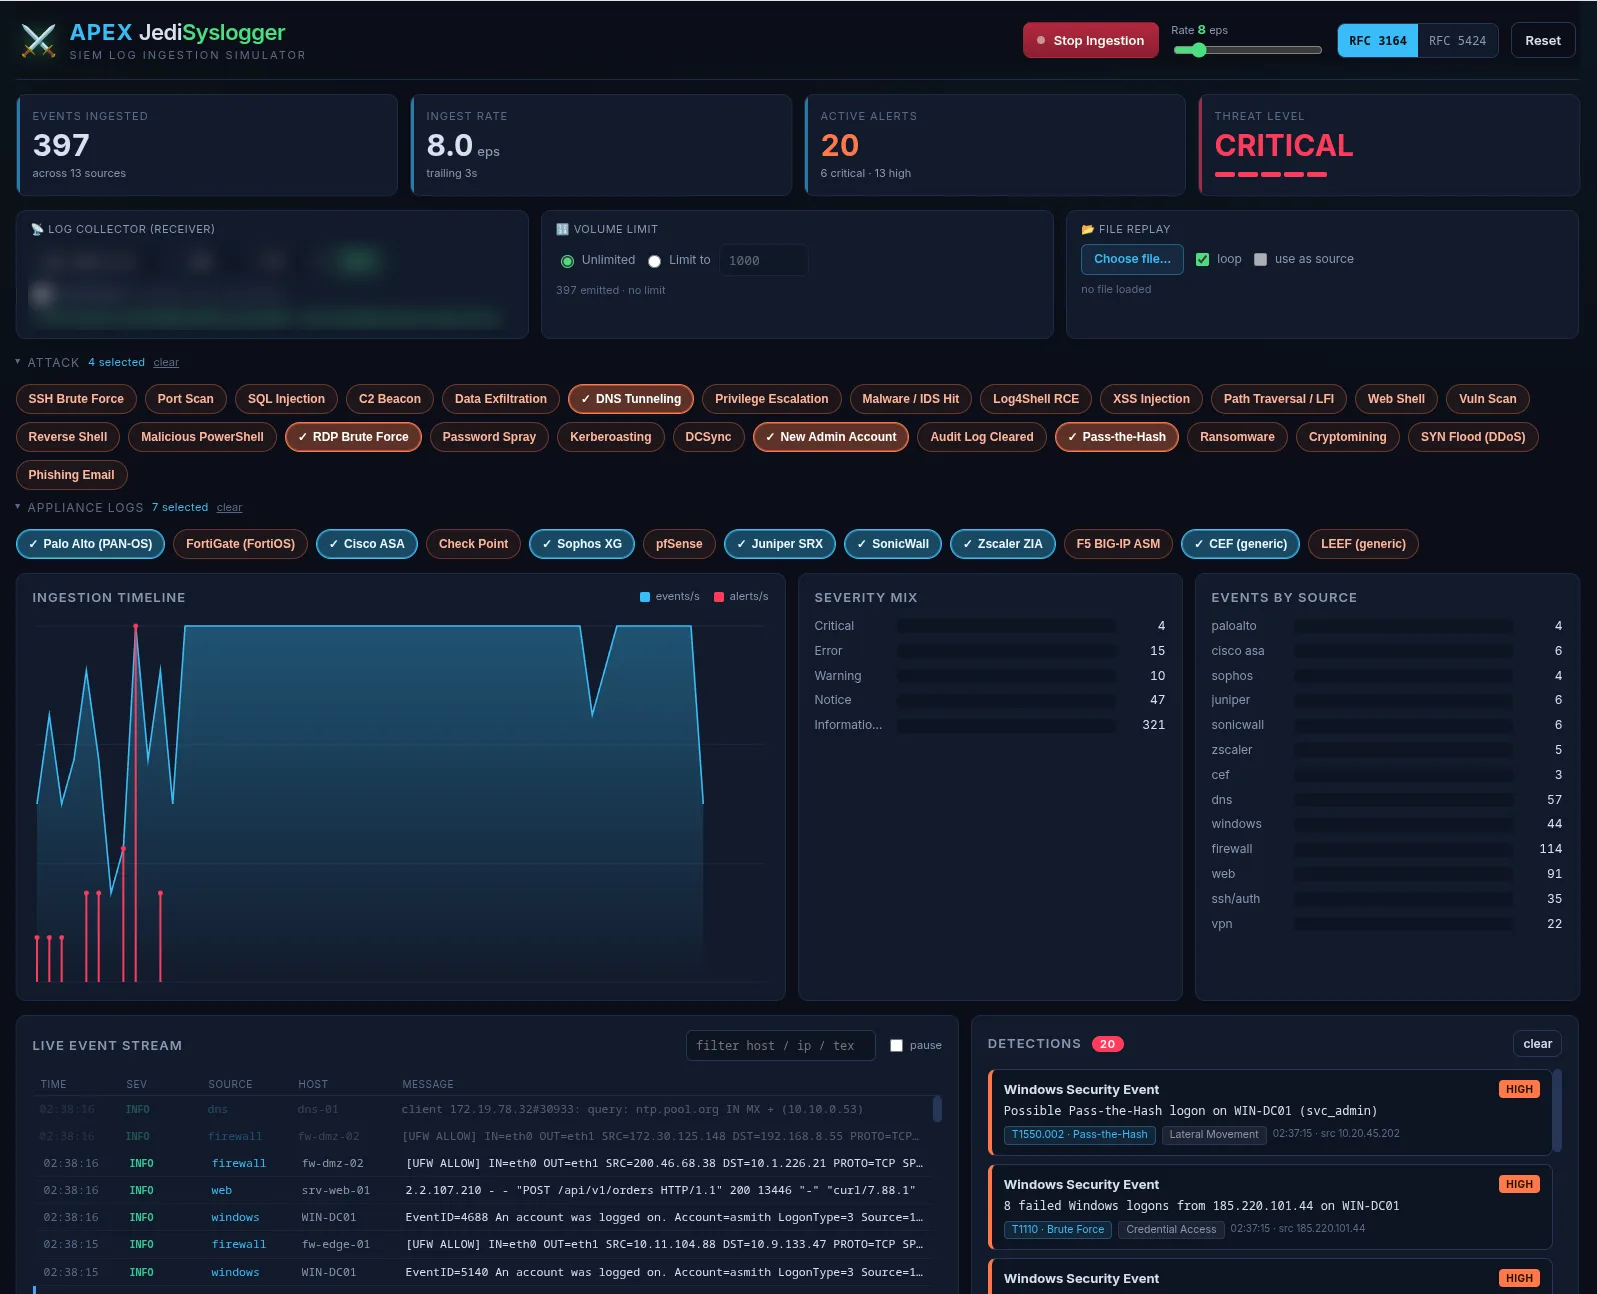
Screenshot of APEX JediSyslogger: event counters, threat level, log stream with appliance events and ATT&CK-tagged alerts
Product screenshot: live log stream, counters, threat level and detections.
56appliance log formats
90attack scenarios
54built-in detection rules
3run modes: desktop, terminal, server

Overview

Detection you can prove

A SIEM can look healthy while missing attacks: a parser changed after an update, a field name does not match a rule, or a rule was never tested against a real attack. These gaps stay silent until an incident.

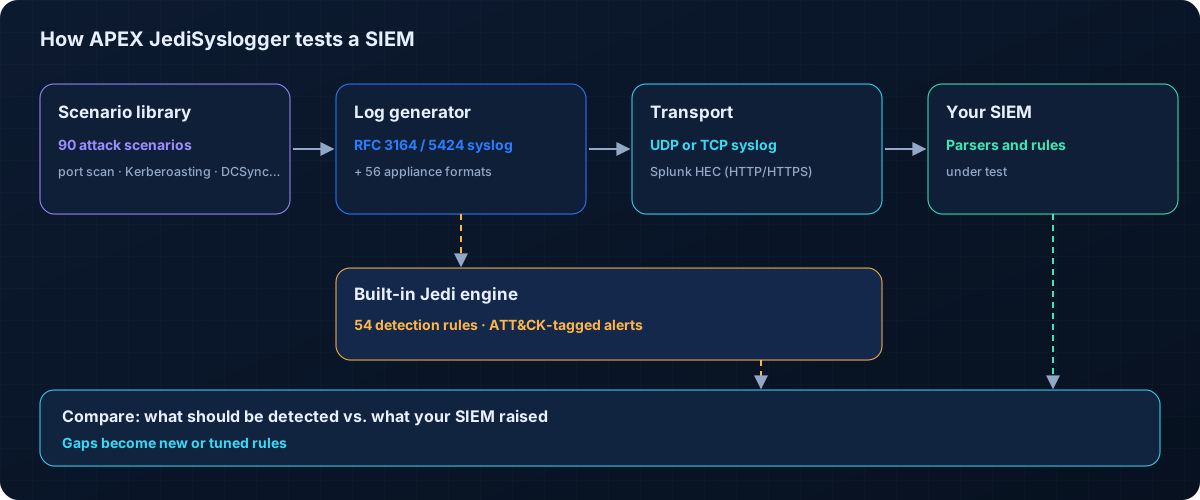
JediSyslogger closes that gap. It produces the logs your environment would produce during an attack, in the formats your SIEM expects, and sends them over the same transports as your real sources. Its own engine raises the alerts that should appear, mapped to MITRE ATT&CK.

Cybercontrol uses JediSyslogger in every SIEM engagement. Security teams also use it to train analysts with realistic data that contains no real customer information.

Capabilities

A complete laboratory for detection engineering

Every capability below exists in the current version of the product.

01

Realistic security log generation

Standard syslog and the native formats of the devices and services in a modern environment.

  • RFC 3164 and RFC 5424 syslog
  • 56 appliance formats: Palo Alto, FortiGate, Cisco ASA/FTD, Check Point, Sophos, Juniper, Zscaler, F5 and more
  • Snort, Suricata, Zeek, BIND, Postfix, Proofpoint, Sysmon, auditd, Windows via Snare
  • AWS CloudTrail and GuardDuty, Azure, Microsoft 365, Entra ID, Defender, CrowdStrike, Okta, Kubernetes audit, CEF, LEEF and OCSF
02

90 attack simulation scenarios

Inject a complete attack into the background traffic and watch it travel through your pipeline.

  • Port scans, brute force, Log4Shell and web attacks
  • Kerberoasting, DCSync, Golden Ticket and Impacket SecretsDump
  • Ransomware, MFA push bombing, impossible travel and mailbox exfiltration
  • Container escape and 11 scenarios for techniques new in ATT&CK v18
03

MITRE ATT&CK mapping

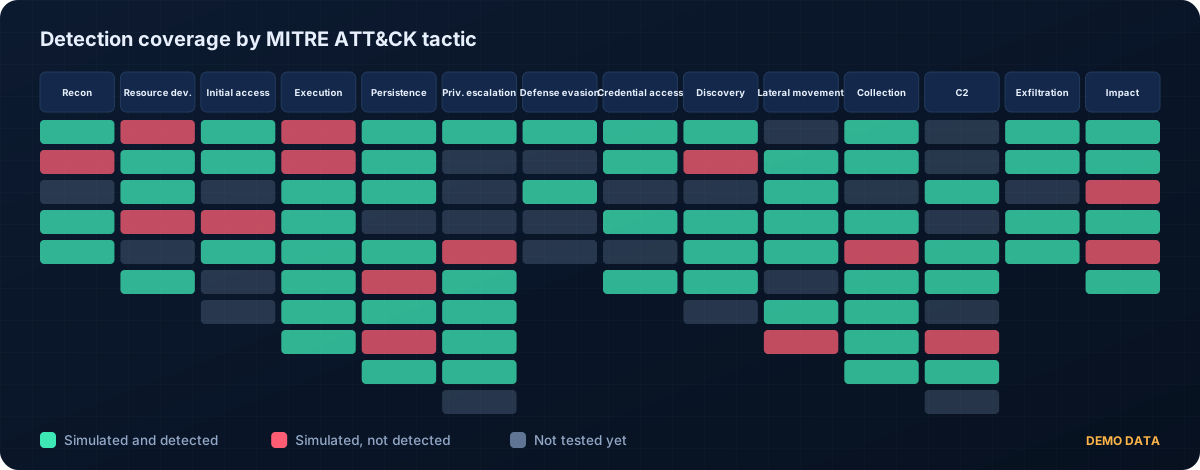
Every scenario and every built-in alert is tagged with the ATT&CK technique it represents.

  • Coverage measured by tactic and technique
  • A threat-level meter from Guarded to Critical
  • A common language between engineers, analysts and management
04

Detection rule validation

The built-in Jedi engine, with 54 stateful rules, shows what should be detected. Compare it with what your SIEM raised.

  • Find rules that never fire and parsers that drop fields
  • Re-test after every SIEM or parser update
  • Turn gaps into new or tuned detection rules
05

Syslog and Splunk HEC integration

Send events exactly as your real sources do.

  • UDP and TCP syslog to any collector
  • Splunk HTTP Event Collector over HTTP or HTTPS, with token, index and sourcetype
  • Connectivity test before sending
  • Event rate from 0 to 60 events per second, volume cap and replay of a log file in a loop
06

SOC analyst training

Realistic data without real customer information, for exercises that feel like a real shift.

  • Repeatable scenarios for exercises and assessments
  • Multi-user server mode, each user with their own settings
  • Terminal mode with JSON output for automated labs

Inside the product

How a detection test works

Pick a scenario, let JediSyslogger generate the logs and send them to your SIEM, then compare its expected detections with the alerts your SIEM raised.

Use cases

Who uses it, and for what

Detection engineering

Build and tune rules against realistic attacks, and prove they fire.

SIEM migrations and upgrades

Re-run the same scenarios before and after a change to catch broken parsers and rules.

SOC training

Give analysts realistic incidents to investigate, with no real customer data.

Audits and assessments

Show evidence of detection coverage mapped to MITRE ATT&CK.

Specifications

Technical specifications

Deployment and integration details of the current version (1.2).

Desktop and terminal

Run it on an engineer's laptop or in a lab, with no server and no sign-in.

Shared server

Multi-user server mode with sign-in and HTTPS, for teams and training rooms.

Log formatsRFC 3164, RFC 5424 and 56 appliance formats
Scenarios90 (83 attack scenarios and 7 special scenarios)
Detection engine54 stateful rules, each tagged with its ATT&CK technique
OutputUDP syslog, TCP syslog, Splunk HEC over HTTP or HTTPS
Rate control0 to 60 events per second, volume cap, log-file replay
Run modesDesktop application, terminal tool jedi (dashboard, headless, JSON), multi-user server with HTTPS
Server securityUser and admin roles, TOTP 2FA, account lockout, scrypt password hashing
PlatformsWindows, macOS and Linux (.deb, .rpm, .pkg.tar.zst, tar.gz, Homebrew)
RequirementsNode.js 18 or later, or the single executable with the runtime built in
Not includedSyslog over TLS is not part of the current version (HEC over HTTPS is)

APEX JediSyslogger

Technical questions

Will it work with our SIEM?

If your SIEM accepts syslog over UDP or TCP, or the Splunk HTTP Event Collector, it can receive JediSyslogger events. The formats follow the vendors' native log layouts, so your existing parsers are tested too.

Does it attack our systems?

No. JediSyslogger only generates log events that describe simulated activity. Nothing is executed against your hosts or network.

Can we use it for analyst training?

Yes. The scenarios are repeatable and contain no real customer data, which makes them suitable for exercises, onboarding and assessments.

Is it suitable for production SIEMs?

Yes, with care: send test events to a dedicated index or tag them, so they can be told apart from real events and excluded from reports.

Find out what your SIEM really detects

Book a demo or a detection-testing engagement, and get a coverage map of your SIEM mapped to MITRE ATT&CK.

Contact

Let's talk about your security

Tell us about your company and what worries you. A specialist will reply with next steps and, if you want, schedule a free initial assessment or a product demo.

What happens next

  • A specialist reads your message and replies
  • A short call to understand your needs
  • A free assessment or a tailored demo

Sending opens your email app with the message ready. Nothing is stored on this website.